DP-600 · 1.1.3 · Maintain a data analytics solution
Fine-grained access
Implement row-level, column-level, object-level, and file-level access control
Restrict Fabric data by object, row, or column when item access is too broad for the audience.
The core idea
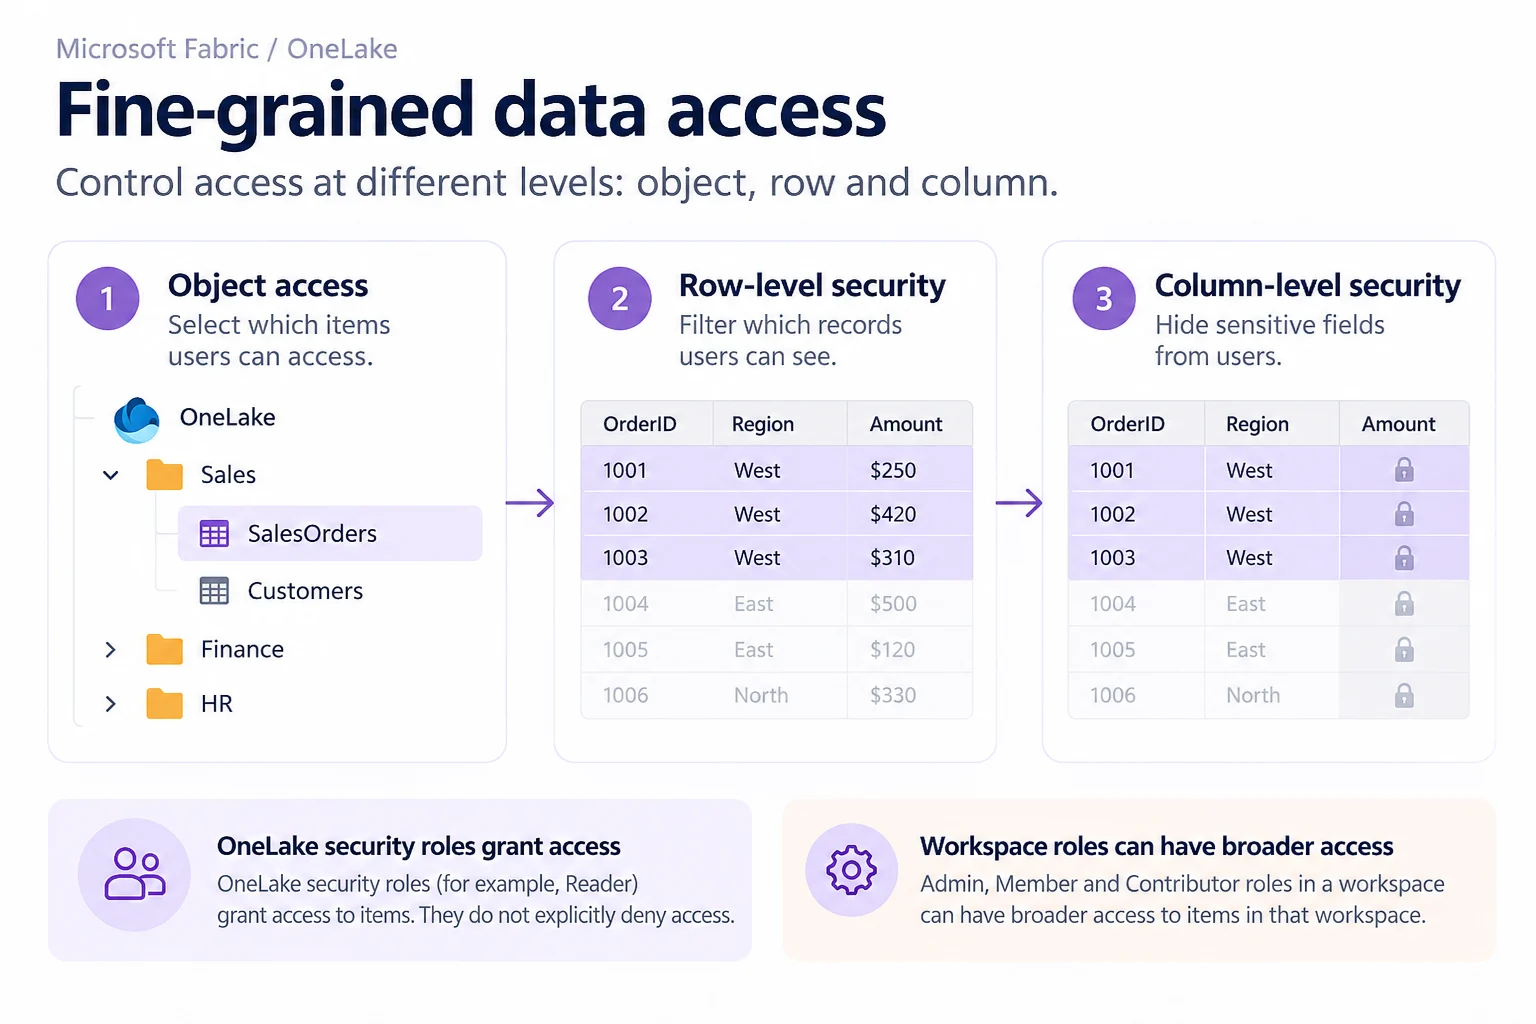
Fine-grained security controls the data plane inside an item. Object access chooses which folders or tables a role can read. filters records. hides selected fields.
security roles grant access rather than deny it. Another role or permission path can therefore still give the same user broader access.
Combine row and column restrictions inside the same role when both are required. Restricted consumers should not also hold broad such as Admin, Member, or Contributor.
Key points
- Object access: limits folders or tables
- : filters which rows a user sees
- : hides selected columns
- : can override intended narrow access
Click an underlined term for a one-line explanation, or see them all in the glossary .
Exam trap
Fine-grained restrictions do not reduce the elevated data access of workspace Admin, Member, or Contributor roles. Design restricted consumers around Viewer or item Read access.
Sources · 2 Microsoft Learn pages Show ▾
Checked on October 4, 2026. Report a problem
Go deeper on Microsoft Learn
Checked against Microsoft Learn on October 4, 2026. Report a problem with this card