DP-600 · 1.1.2 · Maintain a data analytics solution
Item permissions
Implement item-level access controls
Use when access should apply to one Fabric item instead of every item in the workspace.
The core idea
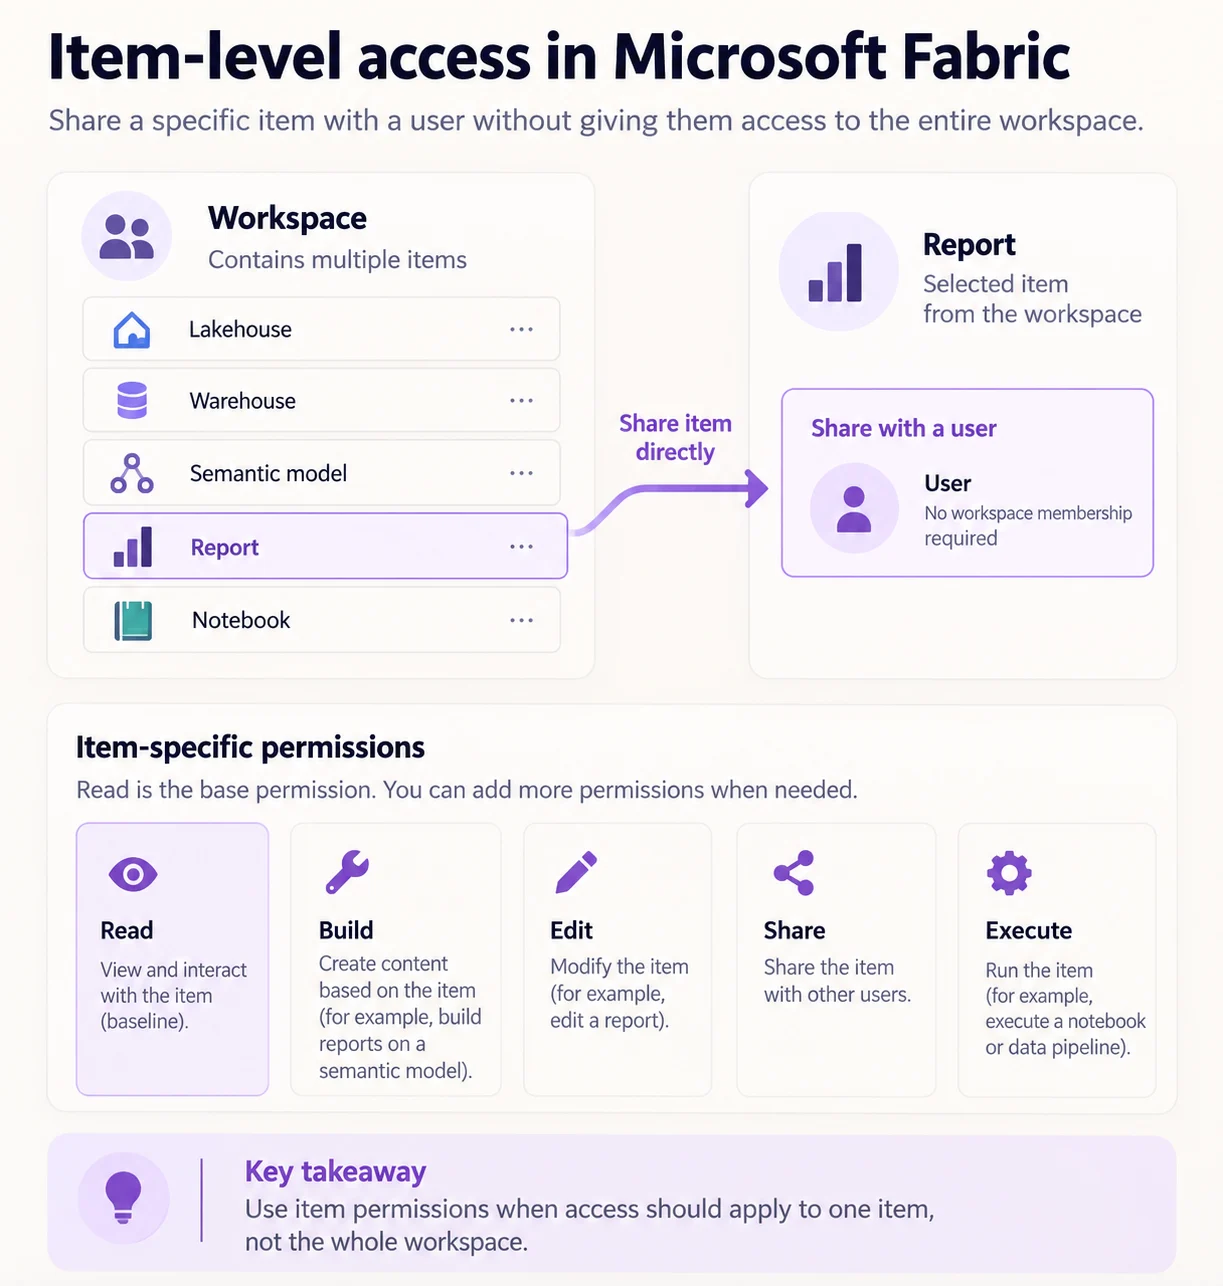
Sharing an item gives access without making the recipient a workspace member. Read is the base permission, and the item can expose additional capabilities such as Build, Edit, Share, or Execute.
The exact permissions depend on the item. Read alone does not automatically grant unrestricted access to underlying or SQL data.
Permissions inherited from a stay broader than direct . Use item-level access when the requirement is intentionally narrow.
Key points
- Item access: grants permissions without workspace membership
- Read: baseline permission for the shared item
- Build: creates new content from a
- Share: lets recipients reshare when permitted
- : can remain broader than item access
Click an underlined term for a one-line explanation, or see them all in the glossary .
Exam trap
Do not assume Read means full access to underlying or SQL data. Additional data permissions can be required for the access path.
Sources · 2 Microsoft Learn pages Show ▾
Checked on October 4, 2026. Report a problem
Go deeper on Microsoft Learn
Checked against Microsoft Learn on October 4, 2026. Report a problem with this card