DP-750 · 2.1.2 · Secure and govern Unity Catalog objects
Fine-grained access
Implement table- and column-level access control and row-level security
Combine grants with row filters, column masks, or governed policies to limit visible data inside a table.
Layer fine-grained controls
- Row filter or column maskRestricts returned data
- Table privilegeAllows the query
- Catalog and schema accessLets the principal reach the object
Fine-grained controls restrict an already authorized query. They do not replace the underlying Unity Catalog privileges.
Rows versus columns
Row filter
- Controls
- Which rows return
- Example
- Assigned region only
- Logic
- Boolean decision
Column mask
- Controls
- Which value returns
- Example
- Hide SSN
- Logic
- Value transformation
Use a row filter when access depends on the row. Use a mask when the row remains visible but one sensitive value must change.
Scale repeated rules
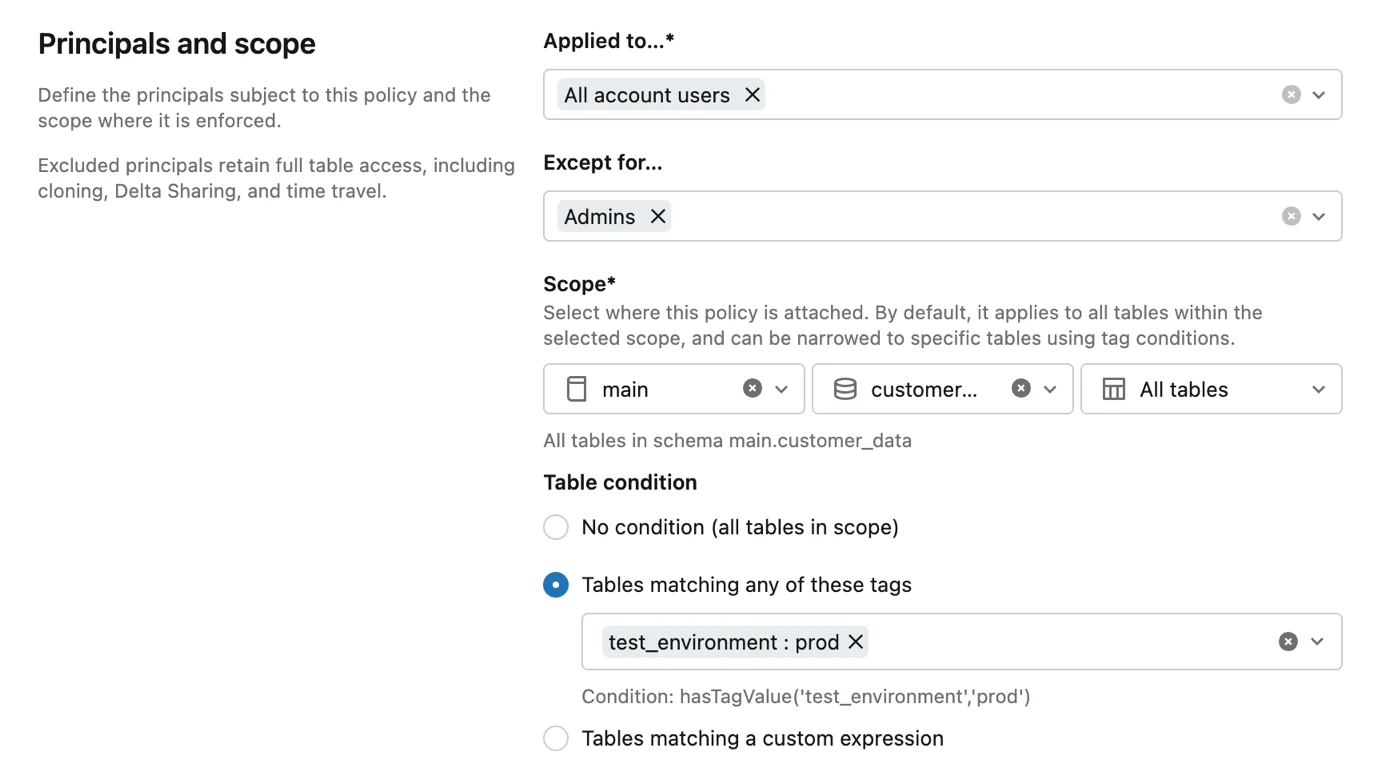
When the same rule should cover many tagged tables, a centralized ABAC policy is easier to govern than duplicating table-specific filters.
Key points
- Table grants: Control whether a principal can access the table
- Row filter: Limits which rows a user sees
- Column mask: Replaces sensitive column values at query time
- ABAC: Scales tag-driven policies across many tables
Exam trap
A row filter restricts rows; it does not grant SELECT on the table.
Sources · 2 Microsoft Learn pages Show ▾
Checked on October 4, 2026. Report a problem
Go deeper on Microsoft Learn
Checked against Microsoft Learn on October 4, 2026. Report a problem with this card